Showing posts with label Office ProPlus. Show all posts

Sunday, November 20, 2016

New ATP Features for Office, SharePoint and OneDrive

There were some new ATP features being released.  For instance there is new reporting capabilities, better performance with lower latency for emails/attachments that are being scanned, deeper URL detonation, and intelligence sharing with Windows Defender.

However, what got be excited is that ATP is being extended beyond Exchange Online.  ATP will now include protection for SharePoint Online, OneDrive for Business, Word, Excel and PowerPoint.  I found this to be really exciting.


Reference
New ATP Features Coming - https://blogs.office.com/2016/09/26/applying-intelligence-to-security-and-compliance-in-office-365/

Sunday, August 21, 2016

Azure Information Protection with Office 365

Introduction
If you are a reader of my blog, you know for the past few years I have been very focused on discussing Office 365 services.  I recently decided to some catching-up on EMS and how it relates to Office 365.  Well as it turns out there have been several recent changes.  One thing that caught my attention very quickly was Azure Information Protection.  In this blog I will explore this solution.

I will say I am super excited to see the vision of this feature given I work with customers who have the most complex security and information protection policies out there.

Note that Azure Information Protection services is currently in Public Preview.

What is the new Azure Information Protection solution?A major challenge that organizations face is protection of their data.  Data loss prevention is constantly on customers’ minds.

With Azure Information Protection we can protect data at the lowest common denominator.  Instead of solely relying on the data storage systems to classify and protect data, we now protect the data directly at the source as email and documents move from place-to-place.

With Azure Information Protection:

  • Classify, label and protect data at the time of creation or modification.
  • Persistent protection travels with the data with rights management.
  • Provide users simple intuitive controls help users make the right decisions and stay productive.
  • Enable safe sharing of data both internally and externally.
  • Ability to create organizational enforceable policies to protect data.
  • Visibility and control over the shared data.
  • Deployment and management flexibility through the cloud.

What is the difference between Azure Information Protection and Azure RMS?
Simply put, Azure Rights Management Services (RMS) got a bunch of new features added to it.  Azure Information Protection building upon RMS with several new capabilities that have been introduced as part of the Secure Islands acquisition.

The new capability that should catch your attention is the intelligent classification and labeling solution that has been integrated with Azure RMS.  This is super exciting capability.

With the new labeling capability in Azure Information Protection services, you have the ability to be able to create enforceable policy to classify and protect your more important critical data.  You have the ability to create labels (classifications) like Personal, Public, Internal, Confidential, Secret, etc.  Then you have the ability to create policies define how data should be tagged with these classifications.  Once data is classified, that data can visual indicators applied to it, RMS protection policies pro-actively applied to the data, and DLP rules (like Exchange transport rules) can watch for this data and take action.

Additionally, there are new reports available to you that allow you to see how the most critical data in your organization is being accessed and managed.  This provides an audit trail for your most critical data.

How can an organization use Azure Information Protection?
Let’s look at Azure Information Protection a little closer.

When a user is in Office, they will see a new ribbon item (Protect) along with new labeling mechanism in the ribbon.  Users have the ability to tag any document or email on the spot.


Administrators have the ability to create the labels that customers see.

Within each label you can:

  • Associate RMS policies you want to apply (if any) to a specific label.  For instance, if you have a Confidential or Secret label, you may want to associate that label to an RMS policy.
  • Create visual markings that would be applied to the email or document once the label is applied.  For instance, add headers, footers, watermarks, etc.
  • Define conditions that could automatically label email and documents.  For instance, if you see data patterns within the content, a label can be auto applied.
There are numerous ways these labels can actually be applied.
  • Automatic – Labels can be applied by IT based on information it can see in the documents and emails.  This means as the user is creating the content, the label can be applied for them. 
  • User Drive – Users have the ability to choose to apply sensitive labels to email or file as they work on it.
  • Recommendation – Instead of automatically applied the label, you can make recommendations to the user on how classify/label.
  • Reclassification – Depending on your policy, you can allow users the ability to re-classify email and documents.  You can even require them to enter a justification which will be logged.
I see endless opportunity for organizations to use Azure Information Protection services to protect their data.  For instance:
  • An organization could create a policy that all documents are automatically classified as Internal.  The Internal does not have to have a RMS policies associated to it, but doing this will set a baseline that all content in the organization has been tagged.
  • As data needs to be become public, the data can be re-classified (labeled) as public by the end user.
  • For documents as classified as Secret or Confidential, an RMS policy could automatically be applied.
  • Re-classification can be allowed without justification for Internal and Public, but for any re-classifications of Secret or Confidential a justification must be provided.
  • I really think there are endless opportunities here with Azure Information Protection services.
How does this relate to Office 365?
As part of the Preview, Azure Information Protection services can be integrated with Office 365 ProPlus.  This means files that you author in Word, Excel, PowerPoint, etc. as well as emails in Outlook will have this user experience.  This will expand with time.

I thought Office 365 already had DLP, where does this play in?
Yes, Office 365 already has DLP capabilities within Exchange Online, SharePoint Online and OneDrive for Business.  Azure Information Protection services provides another layer of protection to data protection along with labeling solution.

For instance, SharePoint Online DLP will identify sensitive documents that were put in a location that has too broad access.  That file can be locked down and then remediated with SharePoint Online DLP by the user or an administrator.  However, what if the end user made a mistake (or worse was malicious) and then tried to send a file tagged as secret outside of the organization?  Azure Information Protection could protect that data tagged as Secret based on your policies.  For instance, you can automatically apply an RMS policy to Secret data and not allow users to re-classify that data.  There are several other mitigations you can take such as watch for documents tagged as secret being emailed externally.

From what I have observed, a challenge customers have had with RMS is educating users on how they should use it.  With Azure Information Protection services classification and labeling solution, the decision has just been super simple for end users.  End users do not need to know complex RMS policies and rule sets; all they need to know are organization contextual tags and the RMS policy is applied for them.

How is Azure Information Protection related to the EMS Suite?
There are two plans, there is Azure Information Protection Plan 1 and Plan 2. 

Plan 1 provides the encryption for files and cloud based file tracking.  From a legacy perspective, this is what you know of as Azure RMS as part of the EMS suite.

Plan 2 adds the new intelligent classification and labeling policies.

There are as well EMS Suites (E3 and E5).  Azure Information Protection Plan 2 is part of the EMS Suite 5.

If you are an Office 365 E3 suite customer, you already get access to Azure RMS service.  However, having Office 365 E3 does not give you access to all the EMS E3 or E5 capabilities.  So to get access to Azure Information Protection Plan 2, to get this new classification and labeling solution, you will need acquire some additional EMS plans.

References
Announcing Azure Information Protection - https://blogs.technet.microsoft.com/enterprisemobility/2016/06/22/announcing-azure-information-protection/
Azure Information Protection Public Review Announcement- https://blogs.technet.microsoft.com/enterprisemobility/2016/07/12/azure-information-protection-public-preview-available-now/
Introducing Enterprise Mobility + Security - https://blogs.technet.microsoft.com/enterprisemobility/2016/07/07/introducing-enterprise-mobility-security/
Acquisition of Secure Islands - http://blogs.microsoft.com/blog/2015/11/09/microsoft-to-acquire-secure-islands-a-leader-in-data-protection-technology
Azure Information Protection product page - https://www.microsoft.com/en-us/cloud-platform/azure-information-protection
What is Azure Information Protection (good video) - https://docs.microsoft.com/en-us/rights-management/information-protection/what-is-information-protection 
Azure Information Protection FAQs - https://docs.microsoft.com/en-us/rights-management/information-protection/faq
Azure Information Protection Quick Start for Preview - https://docs.microsoft.com/en-us/rights-management/information-protection/infoprotect-quick-start-tutorial

Monday, February 15, 2016

Office 2016 Deferred Branch

There was a small change with the Office 365 ProPlus release of Office 2016.  Originally there was:
  • Current Branch – monthly releases of updates would be received by the client.
  • Current Branch for Business – feature updates would be limited to four months.
Apparently after a lot of feedback this was changed to:
  • Current Channel – Formerly Current Branch
  • Deferred Channel – Formerly Current Branch for Business
Public Notification of Name Change - https://blogs.office.com/2016/02/09/deferred-channel-build-now-available-for-the-office-365-client-apps/

Wednesday, December 30, 2015

First Release Program Expansion

The First Release program has some new updates you should be aware of.  This has been a program that I have been following for some time and really like the options this feature provides to Office 365.

The First Release capability allows organizations to be prioritized in receiving updates to the service.  You will receive updates more quickly.  This makes sense for some organizations but sometimes large enterprise organizations with complex IT environments will not want to do it.  A middle ground was introduced several months ago so that “select people” could receive the First Release features which is very helpful for large organizations with complex IT environments.

There have been some recent updates.  SharePoint Online, OneDrive for Business and Office 365 ProPlus have been added to the First Release for Select People.  Exchange Online is already available. 


Resources
Office 365 First Release - https://support.office.com/en-us/article/Office-365-release-options-3B3ADFA4-1777-4FF0-B606-FB8732101F47
Expansion of First Release Program Announcement - https://blogs.office.com/2015/12/08/more-services-join-first-release/
Individual User First Release Announcement - https://blogs.office.com/2015/05/05/manage-change-and-stay-informed-in-office-365/ and http://www.astaticstate.com/2015/05/office-365-first-release-for-specific.html

Monday, December 14, 2015

Office 2016 upgrades for Office 365 ProPlus are coming!

Introduction
If you are an Office 365 ProPlus customer, there is some new planning information that has been published to help get you prepared for the Office 2016 release of Office 365 ProPlus.  Here are some important things that stood out to me.
  • Which Update Branch do you want to use? – There is a new capability that allows you tactically control what types of updates you want push down to devices that have Office 365 ProPlus installed.  Specifically, there is new a delineation between security updates versus feature/bug fix updates.  Some customers want to delay feature/bug fix updates in favor of getting security updates pushed out quickly.  This is a new configuration needs into the Office Deployment Tool.  This is called Current Branch versus Current Branch for Business.
  • New Office Deployment Tool – Yes there is a new tool you need to pull down and work with.
  • How long is Office 2013 still good? - Office 2013 version of Office 365 ProPlus can be used until February 2017.  After that, there will be no longer updates to the Office 2013 version.  This gives enterprise organizations time to roll out Office 2016 to their desktops as a majority of enterprise customers control how updates are pushed.
  • Can you still control updates to 2016 off internal network? – Absolutely, that process does not change.  You still need to do some updates with the Office 2016 Deployment Tool.
  • Downloading Office from Portal – Users that go to the portal will get Office 2013 until Feb 2016.  After that, Office 2016 client would be available for download.
Some other side notes:
  • ProPlus InfoPath 2013 – Note is not part of the Office 2016 Office 365 ProPlus install.  If users still need it, it is available for individual install through the Software page in the Office 365 portal.
  • ProPlus Visio / Project 2013 – Apparently when you upgrade to Office 2016 with Pro ProPlus, the Office 2013 ProPlus Versions of Visio and Project will be removed.  It is not possible to re-install those 2013 version.  You do have the ability to upgrade to Office 2016 ProPlus versions of Visio and Project.
References
Prepare to upgrade Office 365 ProPlus to the Office 2016 version - https://technet.microsoft.com/en-us/library/mt422981.aspx
Overview of update branches for Office 365 ProPlus - https://technet.microsoft.com/en-us/library/mt455210.aspx

Tuesday, November 24, 2015

New Office 365 File Sharing Features in Outlook 2016

With the release of Office 2016 with Office 365, there are new amazing simple features that have been added to the service that will change the way you share Office documents. Sometimes it is these little things have huge impact on how you collaborate.

Up to this point, when you want to share files via email or SharePoint you have had to take a number of steps to share that file. In that past, if you need to solicit feedback on an Office file you have had to take clumsy steps to get that feedback. Sometimes people will take that file, rename, edit it and then email that file back to you. Then you are stuck with multiple versions of a file and you need to bring in all the comments from people back into your file. Worse yet, people will review the wrong versions of the file. You can resolve this issue by simply putting the file in SharePoint however sometimes configuring SharePoint to share a file can be a chore.

So what has changed?

Let’s look at some of these new features.

In Office 2016 there is a new Share button. All you need to do is save your Word, Excel or PowerPoint file to OneDrive for Business or SharePoint. Then press the Share button in Office 2016. You have the ability to select who you want to share the file with, what permissions they have and provide them a message. If you noticed, you no longer need to open a browser to OneDrive for Business, SharePoint or even an email application (Outlook) to share that file; the entire sharing experience is done through Office 2016. Awesome!

Plus moving you can see all the people who have access to the file and modify their permissions right there inside of Office 2016. You do not need to leave Office and navigate to OneDrive for Business or SharePoint to change the permissions making life really easy.

Plus if other people are co-authoring you will see their changes in real-time. Very cool.

clip_image002

Additionally in Office 2016 there is a new Share a Link option. Once you have saved your file to OneDrive for Business or SharePoint, you can press the Share button and get a link to the file right out of Office 2016. You can then provide that link out to a broader audience through whatever mechanism you want versus having to type in tons of names.

clip_image004

Another really simple option you have is in file explorer you can right click on a OneDrive for Business or SharePoint file and click the Share button. This will open the browser where right to the location so you can share that file.

clip_image006

Now let’s pivot the conversation over to some new awesome options available in Outlook 2016 that help you with sharing email file attachments.

First thing you should know about is new capability added to the Attach File button in Outlook 2016. You no longer need to dig around to find the file you were just editing. If the file is saved to OneDrive for Business or SharePoint, you will see that file immediately to easily attach it to your email. Even better, the list is cross device smart. So if you built the file on one device and then try to email it from a different device, you will see that file as a recent edited file for attachment. Frankly I love the ability of not having to go back to SharePoint through the browser to find the file; I can stay in Outlook 2016.

clip_image008

Now here is where things start to get really cool.

Once you have the file from OneDrive for Business or SharePoint attached, you have the ability to set the permissions of the file right there inside of Outlook 2016. Wow! Before I would have to go the location where the file was stored, set the permissions and then come back to Outlook and complete sending of the email. Now I just change the permissions right there on the spot as I am selecting the names of the people that I want to email the file to.

clip_image010

In conclusion these simple examples of new capabilities added to Office 2016 will change the way you share and collaborate with Office documents.

References

https://blogs.office.com/2015/10/05/share-with-the-click-of-a-button-in-office-2016/

https://blogs.office.com/2015/09/22/thenewoffice/

https://blogs.office.com/2015/11/09/attachments-in-outlook-2016-ready-for-collaboration/

Sunday, November 15, 2015

Office for iPad Pro

Office for iPad Pro is coming. You will have Word, Excel, PowerPoint, Outlook and OneNote apps available. This is part of Microsoft’s strategy to provide a rich Office experience across all major platforms. Very exciting.

clip_image002

Public Announcements - https://blogs.office.com/2015/11/11/microsoft-office-apps-are-ready-for-the-ipad-pro/

Saturday, November 15, 2014

Office 365 ProPlus Adding Passive Authentication

There has been a change I have been waiting on that. On the Office 365 Public roadmap it is called “Office 2013 client update to support passive authentication using SAML” - http://office.microsoft.com/en-us/products/office-365-roadmap-FX104343353.aspx.

What is this announcement?

Office 365 ProPlus / Office 2013 will be getting a modification to support 2FA authentication scenarios. This is enabled through the Active Direct Authentication Library (ADAL).

Why is it so important?

There are many customers who require 2FA to authenticate to the Office 365 service. For Office, the Outlook rich client typically comes up a lot because customers want to ensure that users using Outlook use 2FA to receive email. With Outlook today there are scenarios that organizations can implement to ensure there is 2FA with Outlook, however the better long-term solution is to have Office modified to support 2FA directly.

Specifically Office 2013 is changing such that is can support “passive authentication” scenarios in the same way a browser does.

This will enable is a cleaner solution with Office 365 MFA. More importantly it allows for additional support scenarios for organizations who use smart cards (PIV, CaC, etc.) to authenticate to the Office 365 service using the Office 2013 rich client.

What are some facts you should know?

Private Preview Release – Office 365 customers who are in the private preview program can have access to this.

ADAL Authentication – As I mentioned earlier, Office 2013 will be adopting passive authentication in the same way a browser authenticates. If you have AD FS implemented with Office 365, the user will authenticate through that federated trust relationship with Office 365. If you organization requires a second form factor (2FA) for authentication, the user will be required to provide it. A nice side effect of this is Outlook no longer needs to have direct access to the user’s password. Please read this blog for more details on the authentication process - http://office.microsoft.com/en-us/products/office-365-roadmap-FX104343353.aspx.

What Clients are impacted? - Word 2013, Excel 2013, PowerPoint 2013, Lync 2013, Outlook 2013, Publisher 2013, Visio 2013, Access 2013, Project 2013 and OneDrive for Business Sync Client.

Will this work with AD FS Only? – Please review information about other STS providers: http://blogs.office.com/2014/01/30/the-works-with-office-365-identity-program-now-streamlined/ and http://technet.microsoft.com/en-us/library/jj679342.aspx

Office 2010 Support? – No. This solution is for Office 2013 and Office 365 ProPlus.

References

New Announcement – Office 2013 update for SAML and 2FA Auth - http://blogs.office.com/2014/11/12/office-2013-updated-authentication-enabling-multi-factor-authentication-saml-identity-providers/

Original Announcement - http://blogs.office.com/2014/02/10/multi-factor-authentication-for-office-365/

SAML 2.0 Announcement - http://blogs.office.com/2014/03/06/announcing-support-for-saml-2-0-federation-with-office-365/

Outlook Connectivity with MAPI over HTTP Announcement - http://blogs.technet.com/b/exchange/archive/2014/05/09/outlook-connectivity-with-mapi-over-http.aspx

Saturday, November 8, 2014

Office for Android Table

I have to say this has been an extremely active time for Office 365. A significant announcement was announced that Office for Android Tablet is being announced for preview - http://blogs.microsoft.com/blog/2014/11/06/office-everywhere/.

Microsoft has made good on its vision to provide Office across all major mobile platforms. Office is now available on iPhone, iPad, Android Phone, Android Tablet, Windows Phone and Windows tables.

This is amazing.

Organizations can now empower their employees to remain productive where ever they are at without compromises.

Saturday, March 29, 2014

Office for iPad and Office Mobile

There was a major announcement for Office 365 this week that I think almost everyone heard about this week. iPad for Office is now available. For business Office 365 business customers (and consumers) this was long awaited and a proof to world that Microsoft is making a commitment to be a devices and services company. Here are the big facts that everyone should know:

  • Office for iPad supports Word, PowerPoint and Excel.
  • Office for iPad for free allows you to read, view and present.
  • Office for iPad subscription service with Office 365 allows you to create and edit.
  • Office Mobile for iPhone and Android phones is now free, just like on a Windows Phone. No Office 365 subscription is needed.
  • Office for iPad when creating and editing will ensure that content and formatting will be maintained. This is really important for business scenarios to ensure the integrity of documents as a record.
  • Remember all this gets hooked into OneDrive and OneDrive for Business. This means your documents follow you everywhere. I will have to say that OneDrive for Business has literally changed the way I work. When I work with files on my laptop on in OneDrive or any SharePoint Online document library, I have access to all my recently edited Office files on my phone. So when I am on the run, I always have access to what I have been working on. Plus all my OneDrive for Business files accessible from Office Mobile / Office for iPad. Office is not longer just on my PC, it is everywhere I am working across devices. All the Office files (and other file types) are managed in the corporation and are discoverable.

I am telling you. Office Mobile / Office for iPad / OneDrive for Business is literally a game-changer in how your business people work across devices.

Then when you start looking at all the Lync Apps available on Windows Phone, iPhone, iPad and Android you can really see how productive people can really become.

http://blogs.office.com/2014/03/27/announcing-the-office-you-love-now-on-the-ipad/

Saturday, February 15, 2014

Office 365 Power BI is now Generally Available

If you did not hear this week, there was a big announcement that Power BI has now moved into General Availability for Office 365. Please read this announcement - http://blogs.office.com/2014/02/10/power-bi-for-office-365-now-available-to-do-more-with-business-insights-in-excel/.

Now you may be wondering, what is this actually mean if you actually own Office 365 or SharePoint Online Plan 2? I actually found this table right here gave the exact answer I was looking for - http://www.microsoft.com/en-us/powerBI/pricing.aspx#fbid=qNWaVwao6BA.

The core features of Power BI for Office 365 you get:

  • BI Sites
  • Scheduled Data Refresh
  • Enterprise Data Search
  • Data Stewardship
  • Mobile BI
  • Natural Language Query

So if you are an existing E3/E4 customer, you get those features.

Remember with SharePoint Online Plan 2 you already get BI solutions such as Excel Services, Power View and Power Pivot reporting through the browser, etc. For more information read the Service Description here - http://technet.microsoft.com/en-us/library/sharepoint-online-insights-service-description.aspx.

Additionally with Office ProPlus and Excel you get Data Discovery & Access, Data Modeling & Analysis and Visualization which equates to Power Query, Power Pivot, Power View and Power Map.

So you may be asking, what are these new features. I have pulled together some quick references for you to read:

Frankly I need to spin up on this a little bit more, but wanted to get some quick information out to folks…

Tuesday, July 16, 2013

New Office and OWA Apps for iPhone and iPad

New Announcements

Office 365 has again expanded support for iPhone and iPad. There are always been support for ActiveSync for Exchange Online, Lync App, Office Web Apps, SharePoint Online, and OneNote App.

There have been two announcements in June and July 2013 for more solutions for iPhone and iPad. First there was an announcement for Office for iPhone; very similar what users get by default on a Windows Phone. Second there was an announcement for Outlook Web App (OWA) for iPad.

Office for iPhone

Read the announcements, details, and watch a video here - http://blogs.office.com/b/office365tech/archive/2013/06/14/office-mobile-for-iphone.aspx

This capability provides:

  • Integrated log in with your organizational IDs
  • Connect to SharePoint and SkyDrive Pro
  • Word, Excel and PowerPoint (note there is already a OneNote App)

clip_image002

OWA for iPad and iPhone

Hot off the presses, the new Outlook Web App (OWA) for iPhone and iPad. Read the announcements with tons of screenshots and details - http://blogs.office.com/b/office365tech/archive/2013/07/16/owa-for-iphone-and-owa-for-ipad.aspx

This capability provides:

  • Email status notifications
  • Rich email, calendar and contact management
  • Voice commands
  • Information Rights Management support with AD Rights Management Server (AD RMS)
  • Outlook and OWA Apps Support
  • Exchange Online user configuration management
  • And more….

clip_image003

Monday, July 1, 2013

Office 365 Compliance Solutions

Introduction

In this blog I am going to show you some really cool stuff Office 365 can do from a compliance perspective across Exchange Online, SharePoint Online and Lync Online. The great thing about Office 365 is that there are compliance solutions built into across all the technologies. There is retention and records management, archiving, journaling, data loss protection, eDiscovery, Legal Hold, Data Loss Protection and Reporting.

In this blog I am going to show several of these features really quickly from a tenant that I created really quickly.

My objective in this blog is to show you really quickly that Office 365 has really strong compliance solutions which will help an organization have confidence in using Office 365. From this blog I suspect you will want to do deeper reading and analysis on topics.

For deeper information, I recommend you read the following articles from the Office 365 Service Descriptions:

There are tons of links for more detailed information off these three links. Start and you will find a ton of information.

Exchange Online Retention Policies

In Exchange Online you have the ability to create what are called Retention Tags. Tags can be:

  • Assigned as default retention tags for the entire mailbox (one has not been set in the screenshot but it is common to require that all email me maintained for X days).
  • They can be applied to specific folders (like default 30 days retention for Deleted Items folder).
  • Users can be given access to them so they can apply the retention policies themselves (personal retention tags). Users can do this in either Outlook or OWA.
  • There are also archive policies which can be used to move items out of the primary mailbox to the archive mailbox for each user.

Organizations have a lot of flexibility to create policies around how long they want email to be retained.

clip_image002

Once you have created all the retention tags that you want to create, you then have the ability to group those retention tags into a retention policy. Those retention policies are then applied to mailbox users. It is possible to create different policies for different users.

clip_image004

As I mentioned, the policies are available in OWA and Outlook. Below is a screen shot of a how a personal policy can be applied in OWA. Also you can see the email will show the user what is the retention policy that is currently applied to the email.

clip_image006

Side note, if you do not see you retention policies immediately because you created a new tenant or made some changes, run following PowerShell command - Set-Mailbox "username" -RetentionPolicy "Default MRM Policy" - http://technet.microsoft.com/en-us/library/dd298052(v=exchg.150).aspx. This will kick in the policy immediately.

In-Place Archiving

With Exchange Online you have the ability to enable what we call the Personal Archive mailbox. With Exchange Online Plan 2 organizations have the ability to store indefinite amount of data in the Personal Archive.

This is huge for organizations who are really trying to save costs.

  • Microsoft provides the ability to stop having to managing on-premise archiving solutions.
  • It is a solution completely integrated into Exchange Online itself. Users do not have to jump around to do different solutions.
  • End users can have direct access to their archived email.
  • Administrators can search, discovery, retain and place items on legal hold ALL IN ONE PLACE.
  • It provides a solution to avoid having PSTs floating around.

As you can see here, all you need to do is add the personal archive mailbox to a user in the EAC.

clip_image008

Once this is done, the end user will see a second mailbox in Outlook and OWA. As you can see in the OWA screenshot the user can the personal archive. They have the ability to search across both mailboxes with a single query. It is very convenient.

Users can then use personal archive polices or rely on corporate archive policies that will move email from their primary to their archive mailbox. And again, the organization can use retention policies across both the personal and archive mailbox to control how long the email will be retained.

clip_image010

Journaling

Note that it is still possible to set up journaling rules if you want to continue to do journal to an existing archiving solution. This can be quickly set up through the EAC.

clip_image012

Roles Based Access Permissions

It should be noted that in Exchange Online you have ability to control who can have access to all these compliance capabilities. This allows organizations to delegate these duties to specific user. This becomes really import when discussing eDiscovery (which I will be talking about later in this blog).

clip_image014

SharePoint Records Management

Since we were talking about retention management in Exchange Online, it is a good time to discuss records management in SharePoint Online.

The new SharePoint Online the Records Center template is now available in Exchange Online. This is the same capability that people are familiar with SharePoint 2013 on-premise.

You have the ability to create Send To Connections in SharePoint Admin Center (screenshot below). This allows you to send a document from any location to the SharePoint Records center.

clip_image016

I am also commonly asked, is it possible to send email from Exchange Online to the SharePoint Online Records Center. The answer is yes, but you will need to write some code that will move the email and all its metadata to SharePoint Online. It is possible to use the new Apps Model in Outlook 2013 and OWA to write code that will move the email do the drop-off library in the SharePoint Online Records Center. If you are using older versions of Outlook you can write new code that move the item. Really it is just a simple is adding a new button the ribbon and then calling the SharePoint Online REST services to move up the email. There are also some third-party solutions providers that provide these solutions.

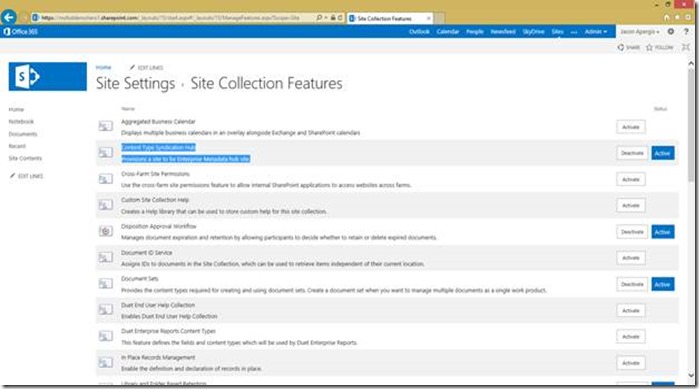
An important part of doing records management in SharePoint is creating common definitions of content. In SharePoint Online the Content Type Hub is supported; all you need to do is turn it on.
clip_image018

Once you turn on the content type hub, you have the ability to create centralized content type definitions and then publish them to all the site collections you have in SharePoint Online.

clip_image020

Here is the records center in SharePoint Online. The only consideration around doing records management in SharePoint Online is understanding your content acquisition strategy. I recommend that your review SharePoint Online storage here - http://office.microsoft.com/en-us/office365-sharepoint-online-enterprise-help/sharepoint-online-software-boundaries-and-limits-HA102694293.aspx. The overall amount of size of the data as well as thresholds on site collections will require organizations to plan on how many record centers will be utilized.

clip_image022

You have the ability to manage the records center just like SharePoint on-premise. You can see here you can manage content types, retention polices, create organizer rules and run reports.

clip_image024

The content type hub is important because when you send data from a site collection to the records center, you want to make sure that all the metadata for the document is maintained. Why? Because you when the document arrives you will want to use that metadata as part of a file plan.

clip_image026

Here is the details of a content organizer rule. In this one it is looking for a specific content type and then looks at the metadata and will store the document the appropriate location.

clip_image028

Then once in the records center you can use all the metadata to navigate through the documents being archived. You can also use SharePoint Search too.

clip_image030

Finally you can run the report in SharePoint Online to get details about the documents that are being stored.

Note another benefit for the content type hub is that you can centrally define retention rules for content type definitions. So when an item arrives in SharePoint Online, the retention rule that was defined centrally will be applied.

clip_image032

SharePoint Site Policies

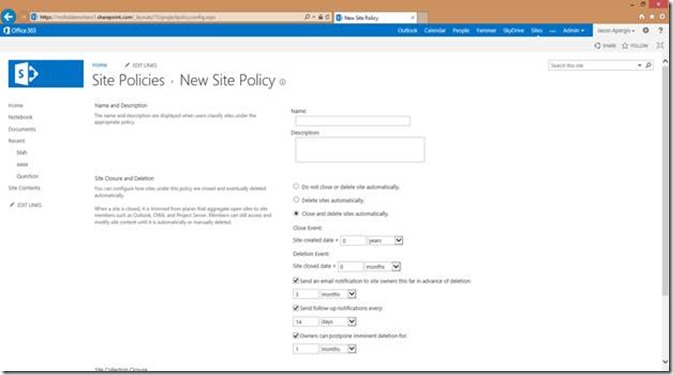
Here is another new capability of SharePoint 2013 that is available in SharePoint Online which has to do with retention. It is common that SharePoint because very popular and there is old content that is being managed. Site Policies do help with governance but they also help from a legal perspective if you need old data to be deleted.
clip_image034

Exchange Multi-Mailbox Search & Legal Hold

Now that we have discussed retention and records management for Exchange and SharePoint Online, let’s discuss Legal Hold.

In Exchange Online there is a built-in capability to do eDiscovery. In the past it was referred to as multi-mailbox search. In the new EAC panel users with permission initiate an eDiscovery and then add a Legal Hold to the items returned in the search.

clip_image036

First you are given a screen to give a name and description to the search.

clip_image038

Next you then scope the eDiscovery search. You can have it go against specific mailboxes or against all of the mailboxes.

clip_image040

Then you can define criteria to find items.

clip_image042

You also have the ability to select which items you want to discover. One thing I like to call out is the Lync items checkbox. This will allow you not only to discuss Exchange items but also Lync items such as instant messages.

clip_image044

This is probably the most interesting screen (below). Once you have defined you query you can then make a decision if you are going to place on a legal hold. There are some options here that are a real game change with the new Exchange Online.

Let’s say that ware going to put the items on legal hold. Here are some options to think through.

  • Indefinite Legal Hold – Pretty simple to understand. If I had not entered any criteria, a legal hold would be placed on the mailbox including Lync items. As new items show up or are deleted by the user they are caught and not deleted until the Legal Hold is released.
  • Query Based Legal Hold – A new capability of Exchange Online is query based legal hold which will only place items that meet the query on legal hold. As new items arrive that meet that query, those items will also be placed on legal hold. This nice thing about this is the entire mailbox does not have to be placed on legal hold.
  • Time Based Legal Hold – As you can also see there is a new option to place a time based legal hold. Think of it as a retention based legal hold. Why is this needed? Many organizations will consider doing this if they business rules that state that no email can be deleted in X days or Y years. The retention policies we discussed early in the blog will place items on retention but a user can still delete items before a retention is complete. A Time Based Legal Hold will complement your retention policies.

As you can see this is really powerful and it is integrated right into Exchange Online. No third solutions needed when you have the archive, eDiscovery and legal hold all in one place.

clip_image046

All of the queries and legal holds are manageable form the EAC. There is an export button in the EAC panel that will generate a PST download of all the data (no more having to connect it to a Outlook <g>).

clip_image048

You also have the ability to see a preview of all the items out of the EAC. If you select preview the search if run again and this screen comes up with allows you to navigate through the data.

clip_image050

SharePoint Online In-Place Hold

Now let’s round out the story with SharePoint Online. First with SharePoint Online Plan 1, there is an In-Place legal hold capability. For SharePoint people, this is actually the eDiscovery and Legal Hold capability that has been around since SharePoint 2010.

When you activate the Hold feature, you will see the Hold features in the Site Collection Administration site. You have the ability to manage all of the legal holds you have run, release them and run reports about those legal holds.

clip_image052

Here is the screen where you can create a search and then optionally place the items on legal hold (or have the items copied to another location).

clip_image054

eDiscovery Center in SharePoint Online

With the new SharePoint Online and if you buy SharePoint Online Plan 2, you have access to the new eDiscovery Center. This is a really powerful capability which allows you to unified eDiscovery and Legal Hold across SharePoint, Exchange and Lync Online all in one location.

On little house keeping item you need to do is add Exchange Online as a source for SharePoint Online to search against.

clip_image056

When you create a new source, you need to select Exchange and AutoDiscover. If you forget to do this, your SharePoint Online eDiscovery Center will not be able to search the Exchange and Lync Online.

clip_image058

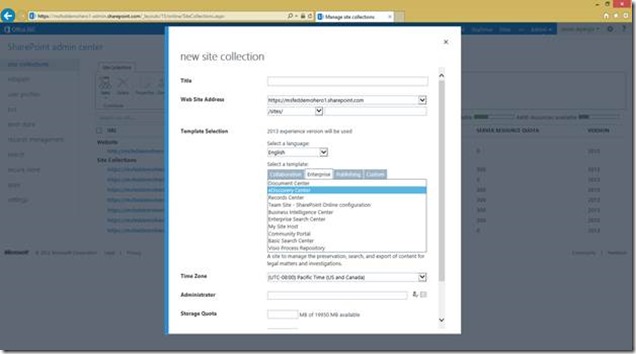
Next you need to create a site collection to do all your eDiscovery from. Just select an eDiscovery Center.
clip_image060

This is what the eDiscovery landing page looks like. From here you can create a new Case.

clip_image062

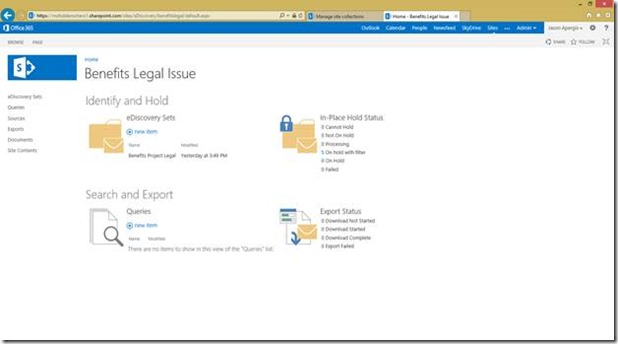
Once your new case has been created, the first thing you need to do identify data sources for eDiscovery on and if you want if you want to place items on Legal Hold.
clip_image064

Here is the page where you will create eDiscovery Set. In here you can see in the Sources I have selected several mailboxes as well as some SharePoint sites. I have also put in some simple criteria (yes you can do complex queries with Boolean logic, etc.). At the bottom you can see that I have option to place items on legal hold or not.

One other new capability of SharePoint 2013 in the cloud is the Preservation Library. It is part of SharePoint Online Plan 2. What this does is if a SharePoint item is placed on legal hold, end users can continue to work on those items. In the past the items on legal hold were locked and the user could not continue to work. The Preservation Library will ensure that if there are deletes or edits to those items, they will be captured, maintained and discoverable.

clip_image066

Here is a screenshot of the of the preview results screen. As you cans see here I can see all of the Exchange and Lync Online data returned in the query. If I were to click on any of the items I can actually see the item right there.

clip_image068

Here is a screenshot of the SharePoint Online items in the preview results. You may notice item in there with the GUID appended to the file name. That is actually an item that met the criteria that is coming out to the preservation library.

clip_image070

Here is something also really neat. If you go back to the Site Collections management screen you will see a lock icon next to one of the site collections. This is basically saying that this site collection cannot be deleted because there are legal holds on within it.

clip_image072

As well, if you go to the Exchange Online EAC, you will see a legal hold with GUID as a title. This is the actual legal hold that was initiated from the SharePoint Online eDiscovery Center.

clip_image074

Once the legal hold has been created, you have the ability to create new searches across the items on legal hold. It is very common to place a broader legal hold and then eDiscovery managers will research and refine the data. Again more searches can created to filter down the results.

clip_image076

Discovery managers can preview the data right in these screens.

clip_image078

Finally Discovery managers can export the data from Exchange, Lync and SharePoint Online.

This is really powerful as it provides organizations the ability a one stop shop to do all of the retention, archiving, eDiscovery and legal hold.

clip_image080

Exchange Online DLP

When it comes to compliance with Office 365, there is still more. We have talked about retention, records, eDiscovery and Legal Hold. Now let’s review some of Data Loss Protection capabilities.

For Exchange Online there is the new DLP solution. With this capability you have the ability to create rules that will inspect email data. This is a new capability that is built on top of Transport Rules in Exchange. The references I provided at the beginning of this blog provide additional information on it.

As you can see here I created a simple policy that will check for SSNs that are sent outside of the organization.

clip_image082

Here is where the rule is defined. One really cool feature of this is you can enable what are called Policy Tips. Policy Tips are displayed to users in Outlook as they author their email. The user will be notified they are violating policy before they actually hit the send button. There are additional rules you can define that will allow the user to send if they provide an explanation, have a manager review the email, etc.

clip_image084

Here is the actual DLP rules that I set up. It is a really basic rule that is looking to SSNs going outside of the organization. It provides some notifications if this occurs. There are tons of other options and operations I could apply to manage. For instance I could block the email all together, require it go through an approval, create exceptions for certain people to still send the email, etc. Again this is a really powerful capability.

clip_image086

AD RMS DLP for Office, Exchange and SharePoint Online

Exchange Online continues to support the ability to work with an AD Rights Management Server (ADS) server that is hosted on-premise.

With the new Office 365, there is the ability purchase an add-on that will host AD RMS in the cloud. Here is a good reference - http://technet.microsoft.com/library/en-us/jj585027.

clip_image088

First all you need to do is activate the AD RMS Service.

clip_image090

Once you have done that, for SharePoint Online you just need to turn in on.

clip_image092

Then in a SharePoint Online document library all you need to do is click on Information Rights Management.

clip_image094

Then you can create an IRM policy. When an Office document is downloaded out of a document library, AD RMS rules will be applied to those documents. This is really powerful if you have content that is being stored in SharePoint that you want to ensure if someone downloads the document, that only people who have rights to the document can view it.

clip_image096

Additionally inside of Office, you have the ability to Restrict Access and apply IRM policies directly to Office.

clip_image098

And the same goes for Exchange Online. In either Outlook or OWA users can put on AD RMS rules on email to ensure the email stays within the organization, cannot be printed, forwarded, etc. You can even create DLP rules that work with AD RMS. For instance if a DLP rule catches an email, it can pro-actively assign an AD RMS policy for the user so if the email does go outside of the organization, no one will be able to read it. Again a very powerful capability.

clip_image100

Reports

Finally the last aspect of compliance I will be covering is reporting. We have covered the important stuff to ensure we can retain, discovery, and place data on legal hold. But in legal situations it is also important to know who has had access to the data.

For Exchange Online (along with the Lync data in the conversation view) there is some good stuff.

First there are auditing reports. There are administrator auditing reports that record actions performed by an administrator as well as mailbox audit logging reports. You can know who has had access to specific mailboxes and actions they may have taken on them.

clip_image102

Additionally there are delivery reports and message trace reports in Exchange Online that helps you track messages.

clip_image104

For SharePoint Online there are Audit Log reports that are available. They can be configured at the Site Collection, Site, Library and documents levels. You can create rules on how long the logs are maintained and where you would like them stored at.

clip_image106

Additionally here are the reports that you can run.

clip_image108

Closing

In closing, I hope this was a good read for you. This was a quick hit on a lot of different topics. As you can see Office 365 does have comprehensive solutions built within the platform that does retention management, records management, eDiscovery, legal hold, data loss prevention and reporting.